Business priorities, independent copies, protected access and tested recovery
What Is a Backup Strategy? RPO, RTO and Restore Testing
A backup strategy is the documented method for deciding what must be protected, how often, for how long, against which failures and how recovery will be verified.
Review Your Backup StrategyShort definition
A backup strategy connects business recovery objectives to copies that can actually be restored
The strategy identifies systems and data, owners, acceptable data loss, required recovery time, copy locations, retention, security, monitoring and test responsibilities. RPO describes the maximum acceptable gap between recoverable data points. RTO describes the target time to restore an agreed service. Backup products and schedules implement part of the plan, but a successful job alone does not prove that credentials, applications, databases and business transactions can be recovered.
Planning scope
Six connected decisions turn backup software into a recovery capability
Systems, data and owners
Servers, endpoints, cloud services, databases, SaaS data, configurations and encryption keys are linked to named business and technical owners.
RPO and RTO
Acceptable data loss and recovery time are set by service importance, dependencies, legal needs and the cost of protection.
Copies and failure domains
Production, local backup, off-site or cloud and offline or immutable copies are separated from common credentials, storage and site failures.
Retention and lifecycle
Daily, weekly, monthly or legal retention is matched to capacity, deletion, versioning, archive and secure disposal requirements.
Security and ransomware resistance
Administrative separation, MFA, least privilege, encryption, immutable settings, network controls and protected keys reduce destructive access.
Monitoring and restore tests
Job failures, missing assets, capacity, stale copies and tampering are alerted, while scheduled restores verify usable outcomes.
Copy design
The 3-2-1 principle is a useful starting point, not a complete architecture
The familiar principle encourages multiple copies, more than one storage type and a copy away from the primary site. Modern strategies often add an offline or immutable copy and require that backup administration cannot be destroyed through the same credentials as production. The exact design depends on data volume, change rate, connectivity, recovery time and threat model.
Copy count alone can be misleading when all copies depend on one identity tenant, storage controller, encryption key or administrator. The design records which failure or attack each copy survives, how long replication delays are, who may delete it and what infrastructure is needed to restore it. Capacity calculations include growth, retention, deduplication assumptions and temporary restore space.
Strategy workflow
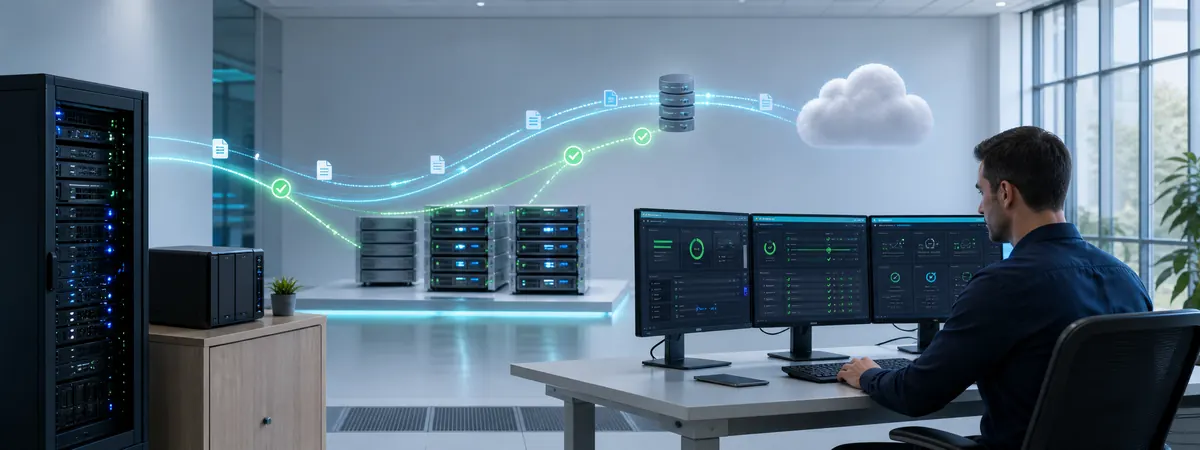
Six stages from business impact to repeatable restore evidence
-
01
Inventory services and dependencies
Record applications, data, configurations, identity, DNS, network, storage, cloud services, owners and operating priority.
-
02
Set recovery objectives
Agree RPO, RTO, minimum service, restoration order and acceptable manual workarounds with business owners.
-
03
Design protection tiers
Choose methods, frequency, retention, copy locations, immutability, encryption and capacity for each service class.
-
04
Secure and monitor the platform
Separate administrative access, protect keys, restrict networks, alert failures and detect assets that are no longer covered.
-
05
Test representative restores
Restore files, systems, databases and applications into isolated targets and validate integrity with the responsible owner.
-
06
Review after change and exercise
Update the inventory, capacity, runbooks and priorities after migrations, new systems, failures or recovery exercises.
Recovery validation
Restore testing must confirm the service, not only the backup file
A restore test starts with a defined scenario and an isolated target. The team checks access to the backup platform, encryption keys, network paths, available compute and storage, restore sequence and required credentials. Database consistency, application start-up, user access, integrations and a representative business transaction are validated by the relevant owners.
Results record the selected recovery point, elapsed time, data gap, manual steps, errors and unresolved dependencies. If the measured result misses RPO or RTO, the strategy changes. Tests should also cover a lost backup server, compromised administrator, unavailable cloud tenant or damaged primary site where those scenarios are relevant.
Strategy record
What a business backup strategy should document
Protection inventory
Systems, data, owners, dependencies, locations, protection method and current coverage status.
Recovery tier matrix
Business priority, RPO, RTO, retention, restore order and minimum acceptable service for each tier.
Copy and security architecture
Targets, failure domains, immutability, encryption, credentials, network controls and deletion authority.
Monitoring and escalation
Job health, missing assets, capacity, stale copies, suspicious changes, owners and response paths.
Recovery runbooks
Access, prerequisites, restoration order, application checks, communication, rollback and escalation steps.
Exercise schedule and evidence
Test scenarios, frequency, owners, measured RPO and RTO, defects, corrective actions and approval.
Useful planning input
Information needed for a backup strategy review
- Systems and data
- Servers, virtual machines, endpoints, databases, SaaS services, cloud resources, configurations and data owners.
- Current protection
- Products, schedules, targets, retention, encryption, immutability, off-site copies, capacity and recent failures.
- Business requirements
- Critical services, operating hours, dependencies, legal retention, acceptable data loss, recovery time and manual alternatives.
- Recovery evidence
- Last restore tests, measured time, application validation, open issues, ransomware concerns and responsible contacts.
Frequently asked questions
What Is a Backup Strategy? FAQ
What is the difference between RPO and RTO?
RPO is the maximum acceptable age of recoverable data, which influences backup or replication frequency. RTO is the target time to restore the agreed service after disruption. Both are business decisions supported by technical design.
Is RAID a backup?
No. RAID can improve availability or tolerate certain disk failures, but it does not provide an independent historical copy against deletion, corruption, ransomware, controller failure or site loss. RAID and backup solve different risks.
Is cloud storage automatically a backup?
Not necessarily. Synchronisation or cloud storage can replicate deletion and corruption. A backup needs controlled recovery points, retention, protected access, monitoring and a restore process appropriate to the service.
How often should restore tests be performed?
Frequency depends on service criticality, rate of change, regulation and risk. Important systems should be tested on a planned schedule and after major architecture, application, credential or backup-platform changes.
Does an immutable backup guarantee recovery from ransomware?
No single control guarantees recovery. Immutability can protect selected copies from alteration for a defined period, but credentials, coverage, clean recovery points, application dependencies, keys, restore capacity and incident procedures still matter.
Can backup strategy reviews be delivered across Turkey?
Yes. Inventory, RPO and RTO workshops, architecture review and test planning can be delivered remotely across Turkey. On-site work is planned when physical media, network, storage or facility conditions require verification.
Official resilience and recovery references
- NIST: Contingency Planning Guide for Federal Information Systems
- NIST: information system contingency planning
- CISA: StopRansomware Guide
Technical review date: . Product capabilities, supported versions, licences and service boundaries are rechecked during project design.
Turn Backup Jobs into a Tested Recovery Plan
Share the systems, data owners, current backup targets, retention and service priorities. We can identify protection gaps and define a practical restore-test plan.