Protective DNS, policy control and investigation-ready logs
Business DNS Filtering and Security Services
We assess the real DNS query path, deploy or improve secure resolver controls, reduce bypass routes and connect DNS events to an operational response process.
Review Your DNS SecurityWhat the control does
DNS filtering evaluates domain risk before a connection is established
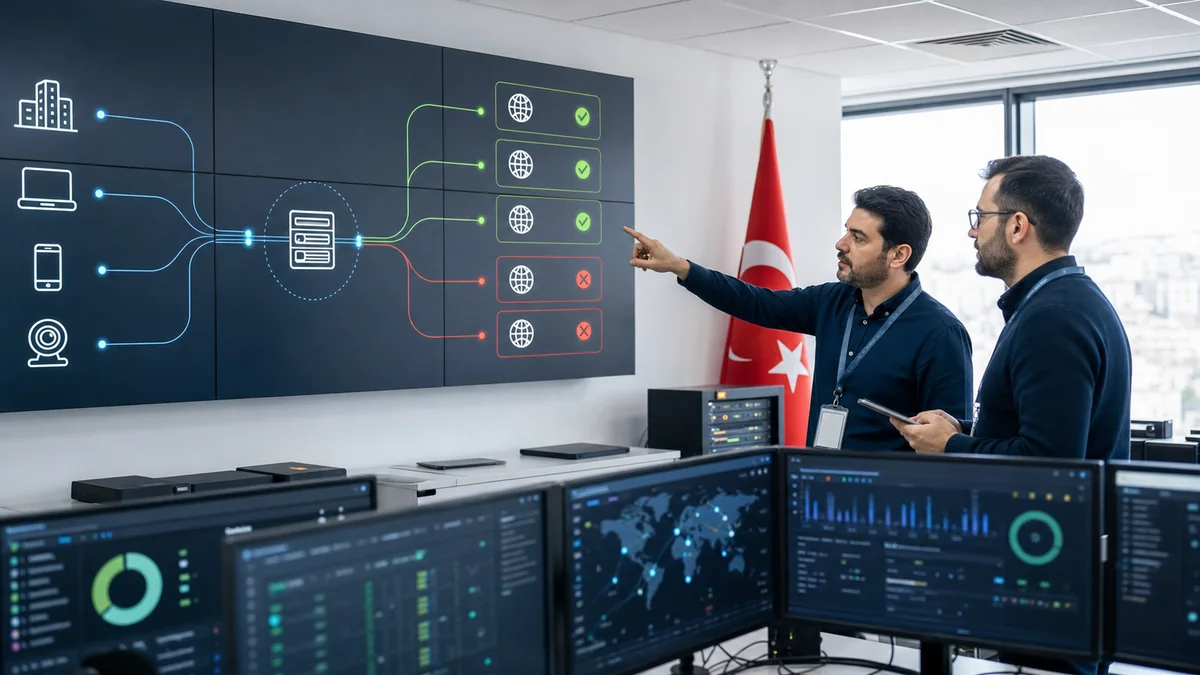
A secure resolver receives a device or user DNS query, checks it against threat intelligence and organisational policy, and then allows, blocks or redirects the response. This can interrupt access to known phishing, malware and command-and-control domains at an early stage. The result is strongest when corporate devices, guest networks, branches and remote users follow an intentional resolver path that cannot be bypassed unnoticed.
Discovery and delivery scope
The DNS path is mapped before policy is changed
Resolver inventory
Client settings, DHCP, Active Directory DNS, forwarders, firewalls, guest networks, VPN clients, branches and cloud workloads are traced.
Identity and policy scope
Sites, users, device groups and network segments are mapped to threat, acceptable-use and exception policies that can be operated consistently.
Resolver architecture
Primary and backup resolvers, forwarding, branch behaviour, remote-user paths and failure handling are designed around continuity and visibility.
DoH and DoT control
Approved encrypted DNS services, browser behaviour, application exceptions and firewall enforcement are reviewed to reduce hidden bypass paths.
Logging and alerting
Query logs, identity context, retention, privacy boundaries, high-confidence detections and transfer to SIEM or incident owners are defined.
Pilot and validation
Representative users and sites are tested first. False positives, resolution delays, failover, remote access and known malicious test domains are checked.
Different controls, different jobs
DNS filtering, DNSSEC and encrypted DNS are complementary
DNS filtering applies threat and access policy to domain queries. DNSSEC lets a validating resolver verify the origin and integrity of signed DNS data. DNS over HTTPS and DNS over TLS encrypt query transport between the client and resolver. None of these controls alone replaces firewall inspection, endpoint security, email protection or a secure web gateway.
Cloudflare's documentation also distinguishes DNS filtering from secure web gateway controls: DNS policy acts at hostname level, while path-level filtering, browser isolation, DLP and content inspection require broader web controls. That boundary is recorded in the solution design so users do not expect DNS policy to inspect every page or file.
Controlled implementation
Six stages from discovery to operational tuning
- 01
Map the current query path
Resolvers, forwarding, DHCP, directory services, branches, VPN users, guest networks and encrypted DNS behaviour are documented.
- 02
Define security and use policies
Threat categories, business restrictions, exceptions, owner approval and different requirements for staff, guests, servers and special systems are agreed.
- 03
Design enforcement and resilience
Resolver selection, identity mapping, failover, firewall rules, remote-user delivery and bypass controls are planned together.
- 04
Pilot representative groups
Policies are applied to a controlled group so business-critical domains, SaaS applications, latency and exception handling can be verified.
- 05
Connect logs and response
High-confidence events, identity, endpoint and network context are routed to the people or platforms responsible for investigation.
- 06
Review and tune
False positives, newly observed bypass paths, policy requests, resolver health and incident outcomes are reviewed on an agreed schedule.
Incident use
A blocked domain is a signal, not a complete incident verdict
The same domain can appear because a user clicked a phishing link, an advertisement loaded a third-party resource, malware attempted command-and-control traffic, a security tool performed a test or a domain was classified incorrectly. Investigation therefore combines the DNS event with endpoint, user, process, firewall, email and timing context.
High-confidence malicious activity is contained and assigned to an owner. False positives follow an exception and review process. The final record states what was observed, which devices or users were affected, what action was taken and whether the policy or another control should change.
Handover
What an operable DNS security handover contains
Resolver and traffic diagram
Client, branch, server, guest and remote-user query paths with primary, backup and forwarding relationships.
Policy and exception register
Applied categories, identity scope, approved exceptions, owners, review dates and the process for requesting a change.
Enforcement record
DHCP, directory, firewall, VPN, endpoint or browser controls that keep approved resolver paths in use.
Logging and retention plan
Log sources, identity fields, retention, access restrictions, SIEM forwarding and privacy responsibilities.
Validation evidence
Resolution, blocking, failover, encrypted DNS, remote-user and representative business application test results.
Operational runbook
Resolver health checks, alert ownership, incident triage, false-positive handling, escalation contacts and review schedule.
Frequently asked questions
DNS Filtering and Security for Business FAQ
What is DNS filtering?
DNS filtering uses a policy-aware resolver to block or redirect queries for malicious, prohibited or otherwise restricted domains before the device connects to the destination. It is an early security layer, not a replacement for endpoint, firewall, email or web security.
Can DNS filtering help against phishing and malware?
It can block known malicious or newly classified domains when users or software attempt to resolve them. Protection depends on the quality and freshness of threat intelligence, correct resolver enforcement and controls against bypass methods.
Are DNSSEC, DoH, DoT and DNS filtering the same thing?
No. DNSSEC validates the authenticity and integrity of signed DNS data. DoH and DoT encrypt DNS transport. DNS filtering applies access and threat policies to queries. A business design may use all three for different purposes.
Why must encrypted DNS be reviewed?
Browsers and applications can use DNS over HTTPS or DNS over TLS. If this traffic is not aligned with the corporate resolver policy, users or malware may bypass filtering and logging. Approved encrypted DNS paths and exceptions should therefore be defined deliberately.
Does DNS filtering block specific web pages?
DNS policy normally works at domain or hostname level. It cannot reliably apply a different decision to every URL path, file or page. Requirements that need content inspection, browser isolation, DLP or path-level controls may require a secure web gateway.
What information is needed for a DNS security review?
We need site and user counts, current DNS servers and forwarders, Active Directory or identity design, branch and remote-user paths, firewall rules, existing logs, cloud services, guest networks, known exceptions and the desired retention and alert process.
Can DNS filtering be delivered across Turkey?
Yes. Resolver, policy, logging and remote-user work can often be designed and supported remotely across Turkey. On-site discovery is arranged when network topology, branch routing or local infrastructure must be verified in person.
Technical references
Current design decisions are checked against vendor and standards guidance:
- Cloudflare: What is DNS filtering?
- Cloudflare Learning Center: DNS filtering and secure DNS
- ICANN: DNSSEC, what it is and why it matters
Technical review date: . Product capabilities and service availability are rechecked during project design.
Discuss Your Requirements with Biga Bilisim
Send the company name, location, current environment, required outcome and preferred timeline. We will review the request and define the most practical next step.